03.1
Registrar
Can suspend the domain name, so the address stops working.
Typical pace
Hours to days
DUBAI · MAZAYA BB2--:--:-- UTC
Brand impersonation · detection & takedown
Perseus Defend protects banks and consumer brands from impersonation. It finds the fake sites and lookalike domains opened in their name, documents each one with evidence captured at detection, and gets it taken down.
87,141Takedowns in the last 3 months
Why lookalikes
Phishing runs on domains bought for the job. Perseus Defend finds them early and gets them taken down.
77%
of the domain names used in phishing were registered by the attacker, not compromised (May 2024 to April 2025).
971,181
phishing attacks observed in Q1 2026, up 13.8% on the previous quarter.
APWG · Phishing Activity Trends Report, Q1 2026(opens in a new tab)
191,561
phishing and spoofing complaints to the FBI in 2025, more than any other crime type.
A takedown request “could take anything between hours to days or even weeks”, says the UK’s National Cyber Security Centre. That is why the evidence has to exist before anyone files.
NCSC · Takedown: removing malicious content to protect your brand(opens in a new tab)
Exhibit 01 · Lookalike check
Type your domain and see the variants an attacker would try first. Computed in your browser; nothing is sent or stored.
12 variants generated for perseusdefend.com
Candidates, not findings: none of these was looked up.
12 of 174 variants for perseusdefend.com.
The full scan our analysts run in the panel is much larger: it tries more domain extensions and checks which variants are already registered.
Talk to an analyst about perseusdefend.comExhibit 02 · One case, start to finish
One lookalike of our demo brand, followed from the moment it is found until it can no longer be reached. The screens are your team’s view of the panel, rebuilt with its own labels.
Every domain sits in one of four states
Threat
A live phishing site. It needs a takedown.
Monitoring
Found and watched: parked, empty or still being checked.
Temporary Takedown
Blocked for now, not yet permanent; we keep at it.
Takedown
Unreachable: blocked, suspended or offline.
“Takedown” means the site can no longer be reached. It does not mean the domain was deleted.
Exhibit 03 · Where a takedown goes
Taking a fake down depends on who controls it. You send one request; we file it with each party that can act on it, then keep checking until the fake stays down.
03.1
Can suspend the domain name, so the address stops working.
Typical pace
Hours to days
03.2
Can take the site’s pages offline.
Typical pace
Hours to days
03.3
Can put a warning in front of the site and pass the report on to its host.
Typical pace
Their own queue
03.4
Can warn visitors before the page opens or drop it from search results. They don’t delete the site.
Typical pace
Their own queue
03.5
Where the law allows, can have access blocked on their country’s networks.
Typical pace
Their own procedure
03.6
Can remove an account that impersonates your brand.
Typical pace
Each platform’s own queue
Finding, documenting and classifying a fake runs on our clock. Taking it down runs on the clock of whoever hosts or lists it, and nobody can promise their pace.
Our part
Find, document, classify
As soon as it is found
Your decision
The takedown request
Whenever you send it
Their part
The parties that host or list it
Hours to days, sometimes weeks
Time after the fake is found · log scale
Timings describe typical behaviour, not guarantees: every party works to its own rules and pace. The UK’s NCSC puts takedown at anywhere from hours to days, or even weeks. NCSC
Exhibit 04 · The panel, uncropped
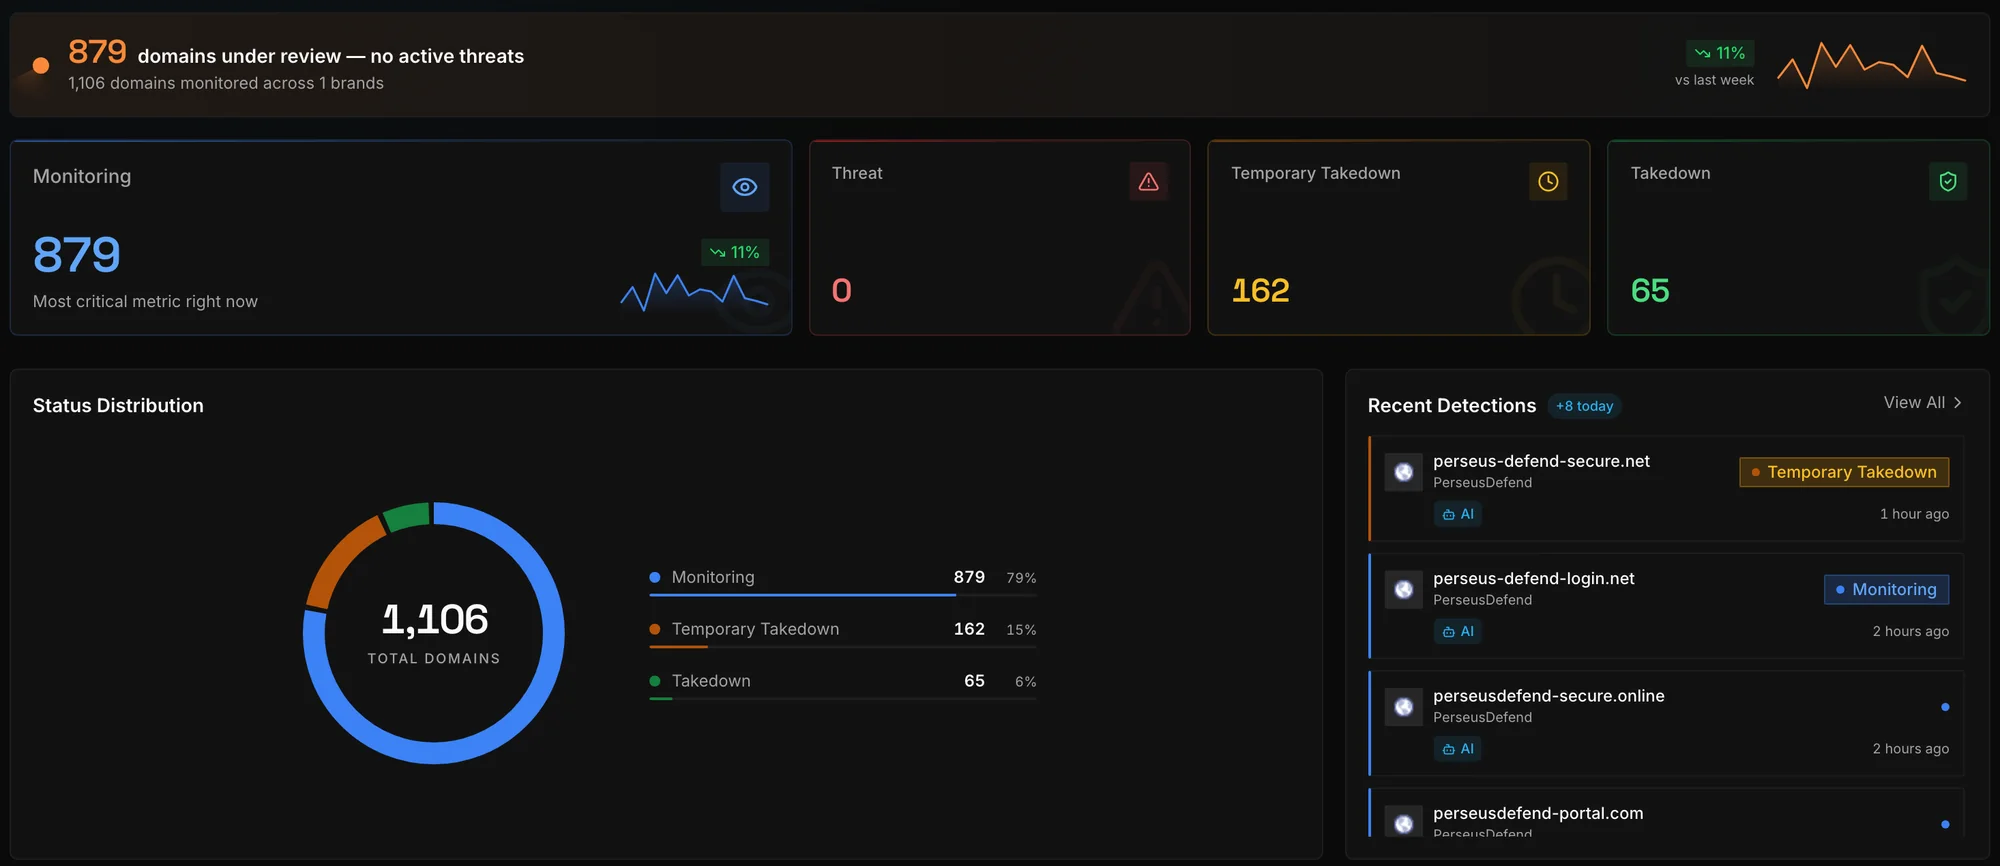
Exhibit 05 · The film
All data in the film is an anonymised replay.
Music: “Inspired” by Kevin MacLeod (incompetech.com), licensed under CC BY 4.0
73 seconds in the panel, with anonymised data: the daily overview, the threat list, the screenshot kept as evidence, the takedown request and the case that follows it.
Chapters
OpeningYour customers may be transacting on a fake copy of your site right now. And before you notice, your brand’s reputation is at risk.
Overview: what is happening today?Perseus Defend finds fake sites opened in your brand’s name, documents them and gets them taken down. The panel is the daily summary: is a threat live, how many domains are in which state. Let’s follow this domain from recent detections.
The threat listEvery record the AI finds sits on one row with brand, detection date and status. Here is the domain we are following.
Evidence: the screenshotThe screenshot taken at detection time is kept as evidence: is it really a copy of your site, at a glance.
The takedown requestThe takedown request comes from a single menu: confirm the domain, add a note, send. Bulk sending is possible too.
Case trackingThe request becomes a case; which channel, when, and what came back, all here in order.
ClosingDetect faster. Take down sooner. Perseus Defend.
Lookalike domains and cloned websites that use your brand, plus the fake social media accounts you point us to, which are added to your panel by URL.
Our part runs as soon as a domain is found: the site is documented with evidence and classified. Once a takedown is filed, the parties that register and host the fake set the pace, usually hours to days.
Every AI verdict is stored with its confidence score and the screenshot taken at detection, so a person can check it. Your own and partner domains go on the Whitelist and are not flagged again. Nothing is filed without a takedown request, and a request can wait for approval before it goes out.
Finding, documenting and classifying are automatic. The takedown request is raised in the panel by your team or by our analysts, and in some setups it is raised automatically. We then file the case with every party that can act on it.
The case doesn’t rest on one party. Where it qualifies, it also goes to the other parties that can block access to the site: security and blocklist providers and the relevant authorities. We keep checking the site until it stays down.
That the site can no longer be reached. It doesn’t necessarily mean the domain was deleted, and we don’t report it that way. If a closed site comes back, it is picked up again.
In your panel, each record keeps the screenshot captured at detection, the registrar, the IP owner, the detection date and the status. Lists export as PDF, CSV, Excel or JSON.
Each client works in its own tenant: your records are visible to your team and to our analysts, not to other clients. Personal data is processed in line with KVKK and GDPR; see our privacy policy for the details.
You talk with one of our analysts. We walk you through the panel and look at your domain together, so you can see how a case would run for your brand.
Dossier
Next case
perseusdefend-giris.com · Takedown
Tell us which brand you need to protect. We’ll walk you through the panel and follow one case from detection to takedown.